Checksum Crown
A vault token combines an encoded claim with an integrity value. Determine whether that value depends on anything unavailable to the token holder.
Objective
- Reproduce a client-visible checksum over a modified claim.
- Distinguish error detection from keyed authentication.
Before you begin
Open /challenge/hard/checksum. Preserve pctf_session; work only with the separate vault token.
Concepts
An unkeyed checksum can detect accidental changes, but anyone who edits the message can recompute it. A MAC binds data to a secret held by the verifier.
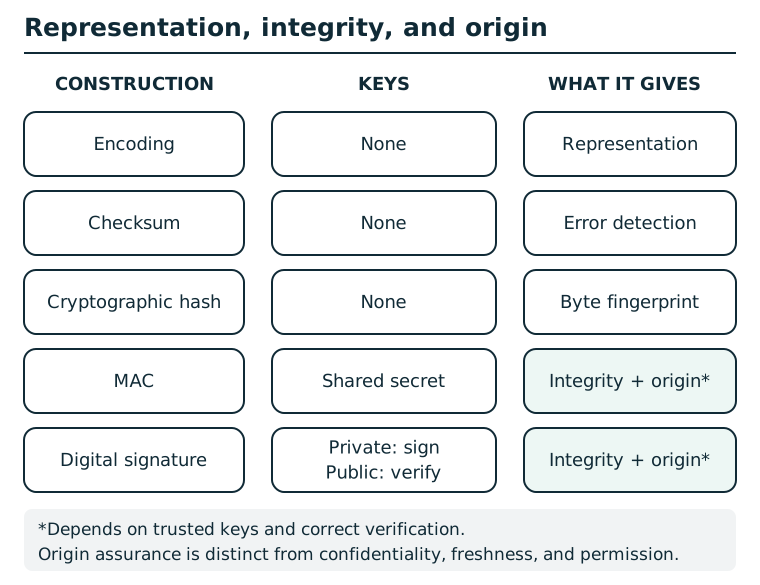
Encoding is reversible. Checksums detect accidental errors. Hashes fingerprint bytes but do not authenticate a source. A MAC provides integrity and origin within a group that shares a secret; any member can create tags. A signature binds bytes to a private-key holder when verification and public-key trust are correct. None of these alone encrypts, proves freshness, or grants authorization.
Suggested tools
- Storage and source inspectors: Separate the token and read its loaded JavaScript. Python can reproduce the small checksum locally.
Tool practice
Rehearse the worked tool exercise before using challenge data.
Print the decoded payload with repr and compare its byte length before calculating. The checksum script encodes that decoded text as UTF-8; it does not sum the characters of the Base64 wrapper. Reproduce the original checksum first, then consider a changed claim.
Investigation
Observe
Split the token at its separator, decode the payload, and inspect the script's integrity algorithm.
Form a hypothesis
Can you replace the ordinary role with the privileged role and calculate a matching integrity value without a server secret?
Test carefully
Preserve the token's two-part format and change only the authorization claim.
Progressive hints
Hint 1
Decode the first component and open the loaded script.
Hint 2
The script sums the decoded payload's UTF-8 bytes modulo 65,536, not the Base64 wrapper's characters.
Hint 3
Encode the privileged payload and format its new checksum as four hex digits.
Troubleshooting and reset
Use lowercase, zero-padded hexadecimal and retain Base64 padding. Delete only vault_token to receive a fresh ordinary token.