Profile Overflow
A profile endpoint maps submitted form fields onto an account. Test whether it accepts a security-sensitive field that the visible form never offered.
Objective
- Add one unoffered field to a normal form request.
- Explain how field allowlists prevent mass assignment.
Before you begin
Open /challenge/medium/profile and submit the ordinary form once while the Network panel records it.
Concepts
Binding every supplied field to a model can expose internal properties. A safe handler explicitly permits only fields the operation is intended to change.
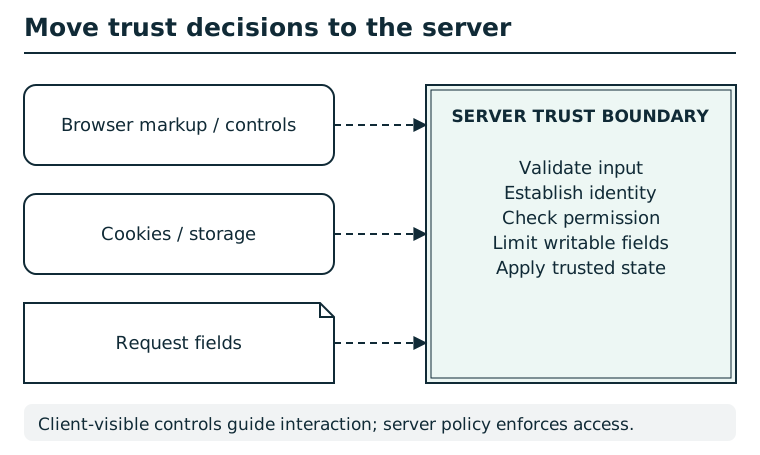
The browser can change local markup, storage, cookies, and request fields. Hiding a control or trusting a client-supplied role does not enforce permission. The server validates input, establishes identity, checks authorization, and limits writable fields before changing trusted state. A signed client value still needs correct verification, scope, and freshness checks.
Suggested tools
- Network inspector or HTTP client: Reproduce the normal encoded form body and add one field while retaining the ordinary values.
Tool practice
Rehearse the worked tool exercise before using challenge data.
Capture the normal POST and record each form field. Reproduce it unchanged before adding one field with a separate --data-urlencode argument. Inspect the outgoing payload to confirm you sent form data, not JSON or a query parameter.
Investigation
Observe
Record the endpoint, method, content type, and offered fields. Identify the account property the page says must never be client-assignable.
Form a hypothesis
Will the handler bind that extra property even though the form omitted it?
Test carefully
Copy a legitimate request and add only the role field with the privileged role established earlier in the profile.
Progressive hints
Hint 1
Inspect the POST body sent by the normal form.
Hint 2
The omitted field is the account role.
Hint 3
Add that field using the higher role named earlier.
Troubleshooting and reset
Use URL-encoded form data with the original display name and theme. This training account is request-local, so another normal submission is safe.